
On October 21, the PHP project shipped an urgent security release for two critical remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, now widely nicknamed PHP2Shell. If your product runs on PHP, which includes every Laravel application, the practical question this week is how much of your estate you can honestly call patched and running the […]
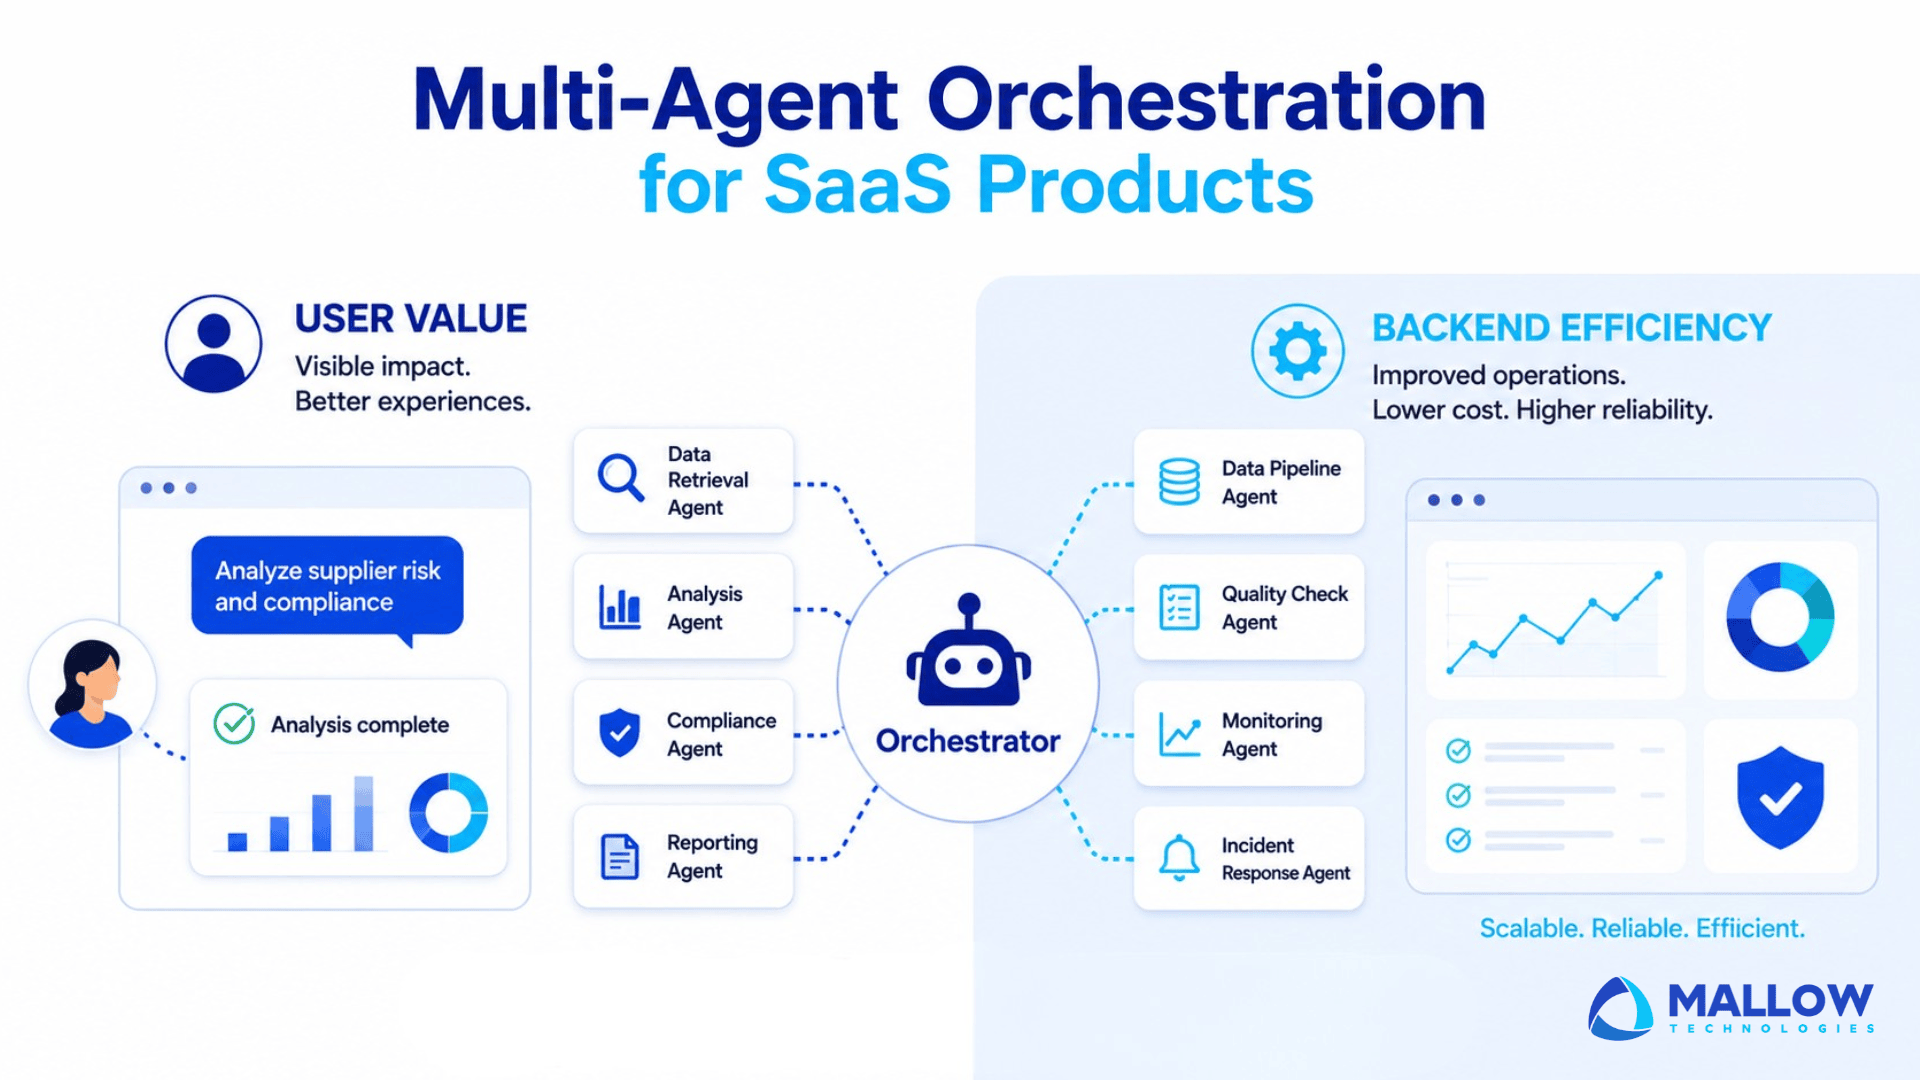
There is a version of this conversation that goes very well in a board meeting. “We’re building multi-agent AI.” It sounds sophisticated. It signals technical ambition. It gets nodded at by investors who have just read about it in three different newsletters. The problem is that many SaaS teams building multi-agent systems right now are […]
Implementing robust security practices is essential for protecting your Laravel application, safeguarding sensitive information, and maintaining user trust. Developers need to review application security regularly as frameworks, dependencies, and potential attack methods evolve. At Mallow, we combine technical expertise with an understanding of the challenges involved in developing and maintaining Laravel applications. This article covers […]
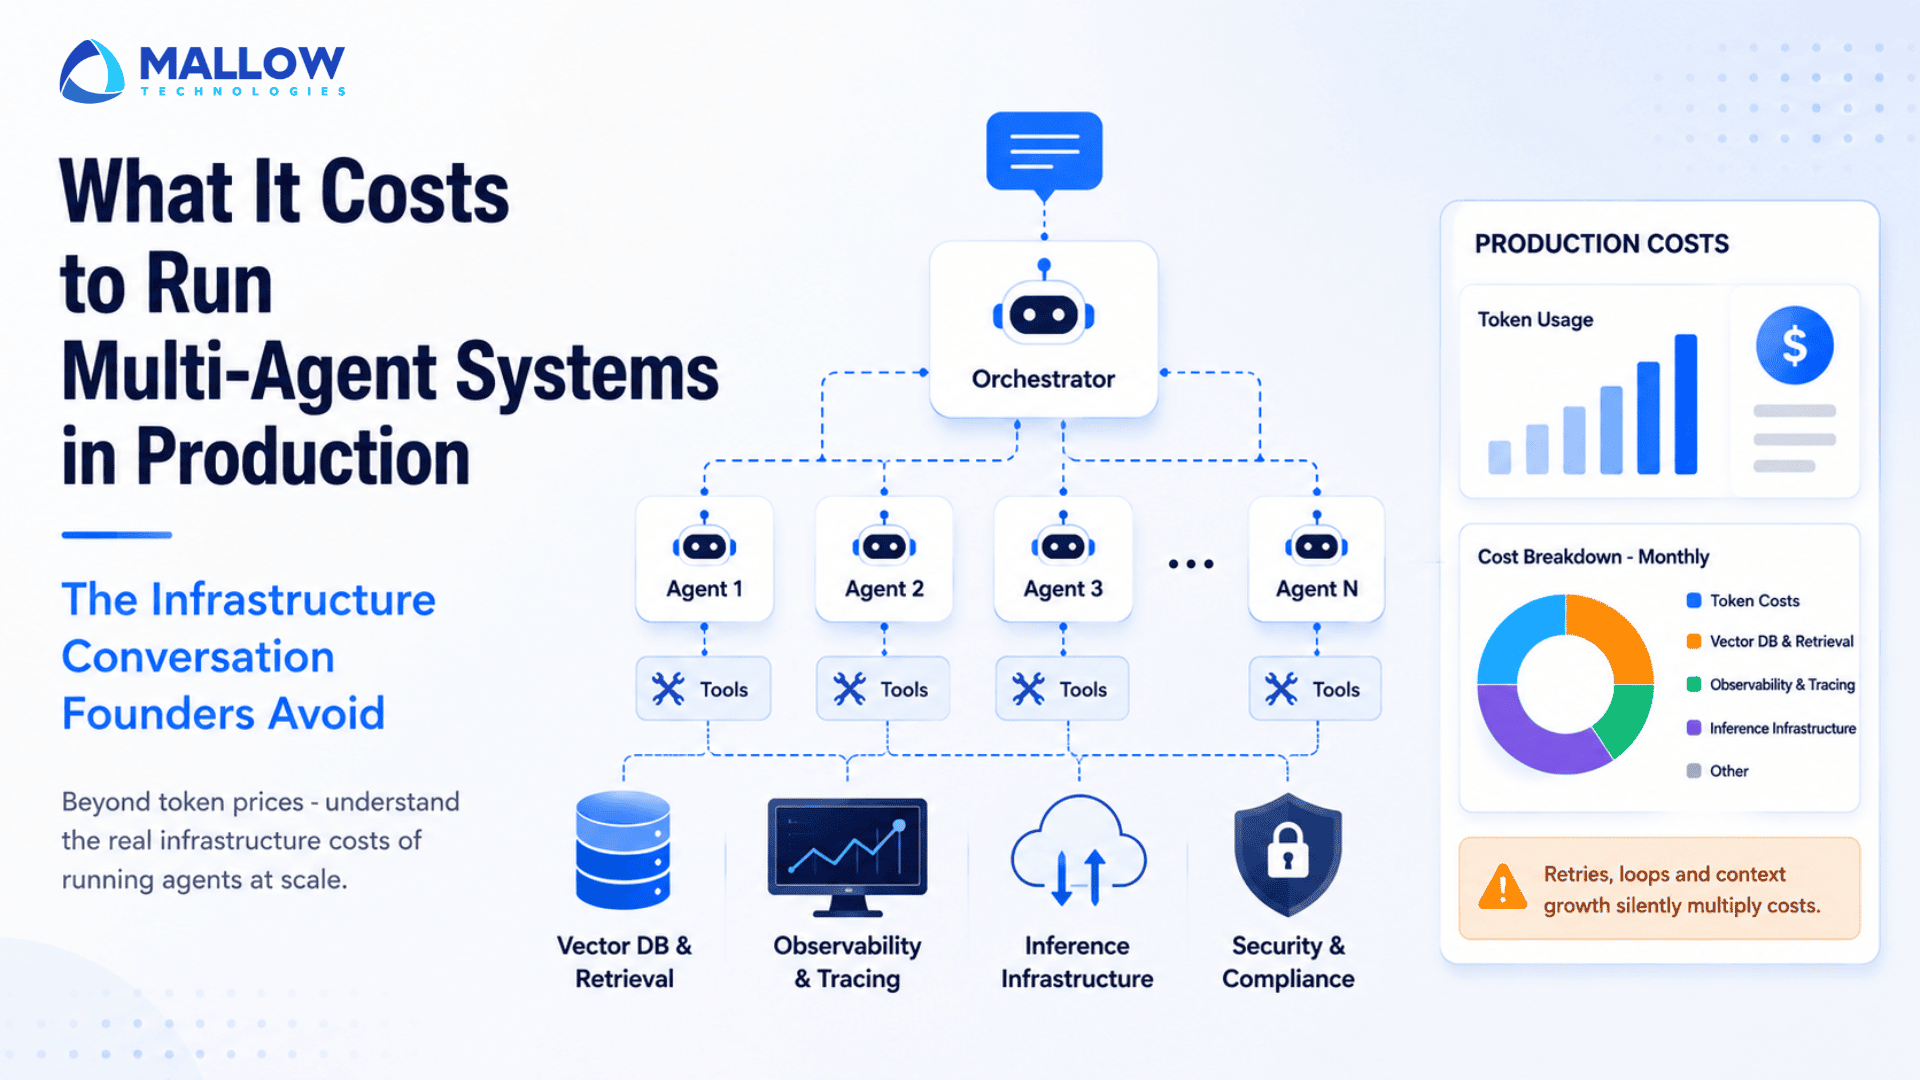
The conversation founders avoid is not the one about whether to build with agentic AI. That conversation has largely been settled. Most teams have approved a build or are close to it. The conversation they avoid is the one about what it will cost to run after it ships. Most production cost models for agent […]
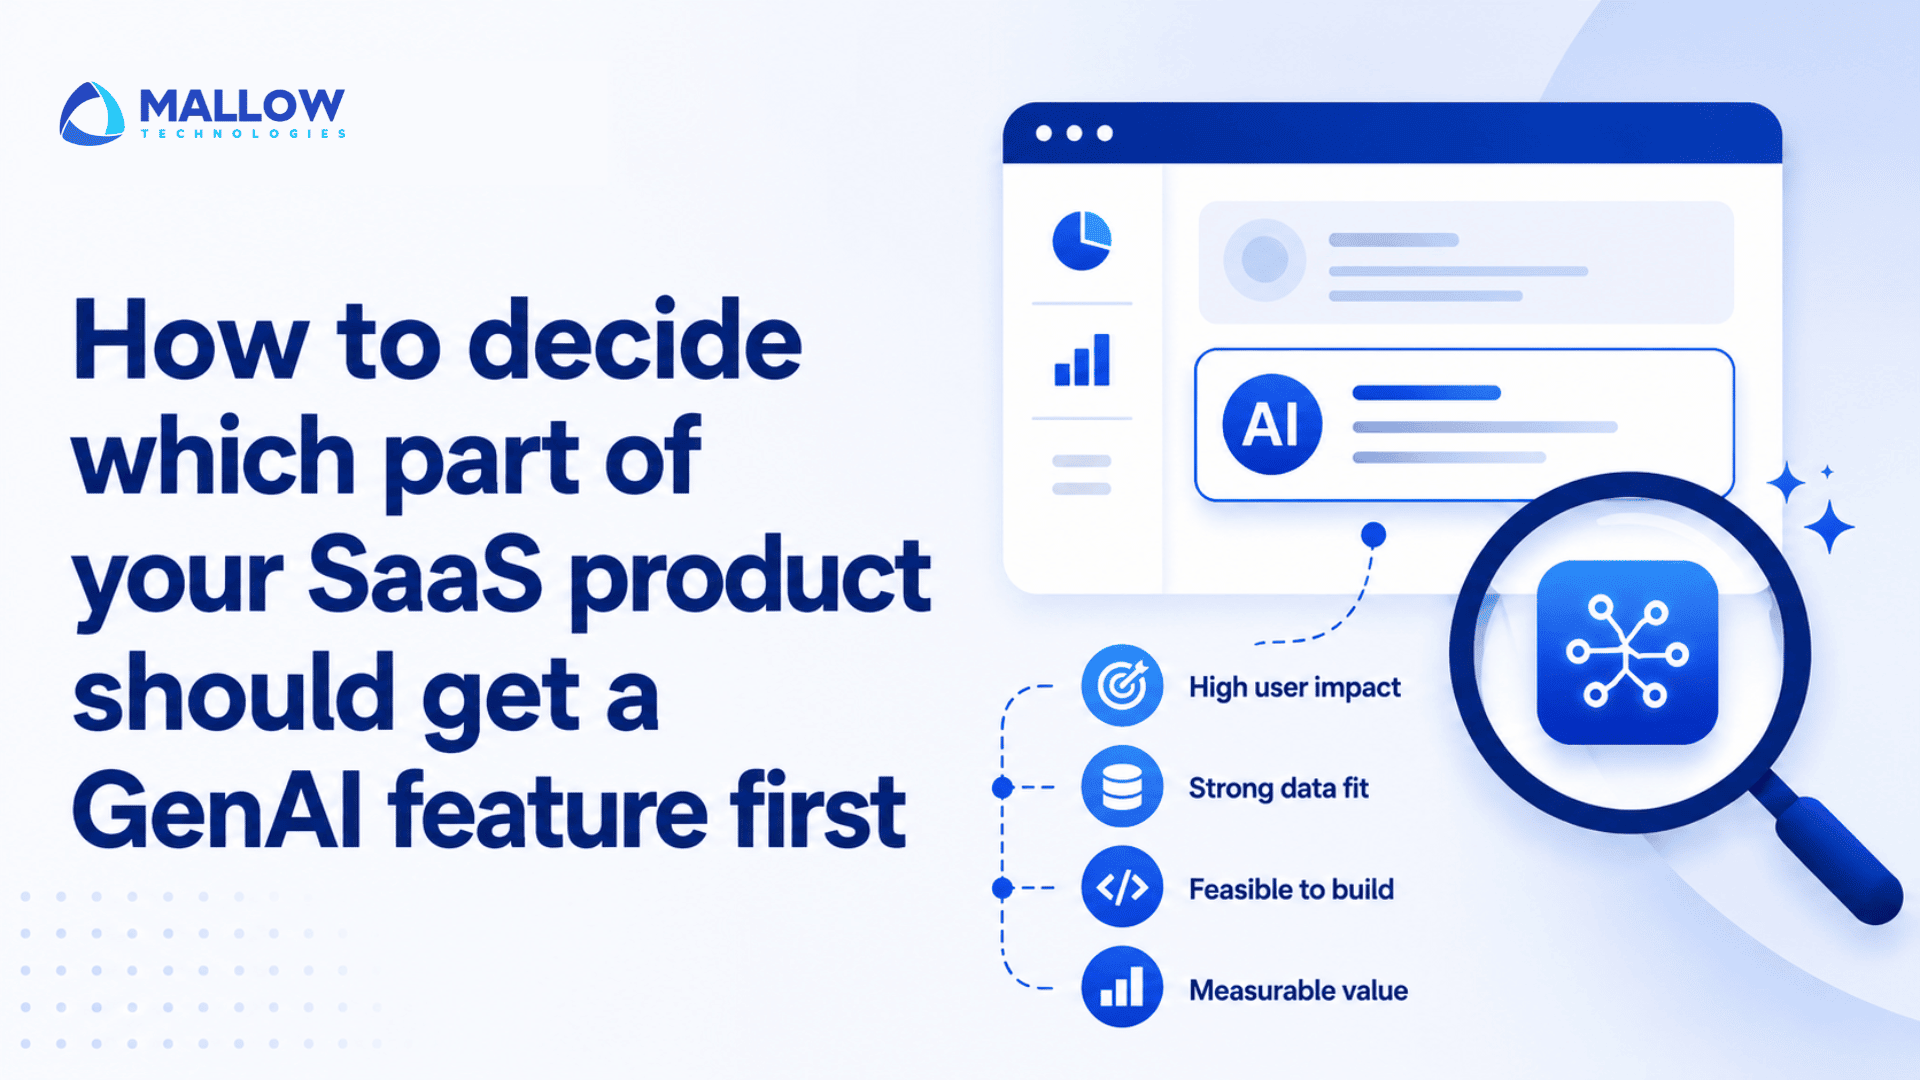
There is a version of this decision that happens in a sprint planning meeting. Someone mentions that a competitor just shipped an AI summary feature. Another person suggests adding one to the dashboard. Everyone agrees it sounds good. It gets added to the roadmap. Engineering starts work three weeks later. There is another version where […]
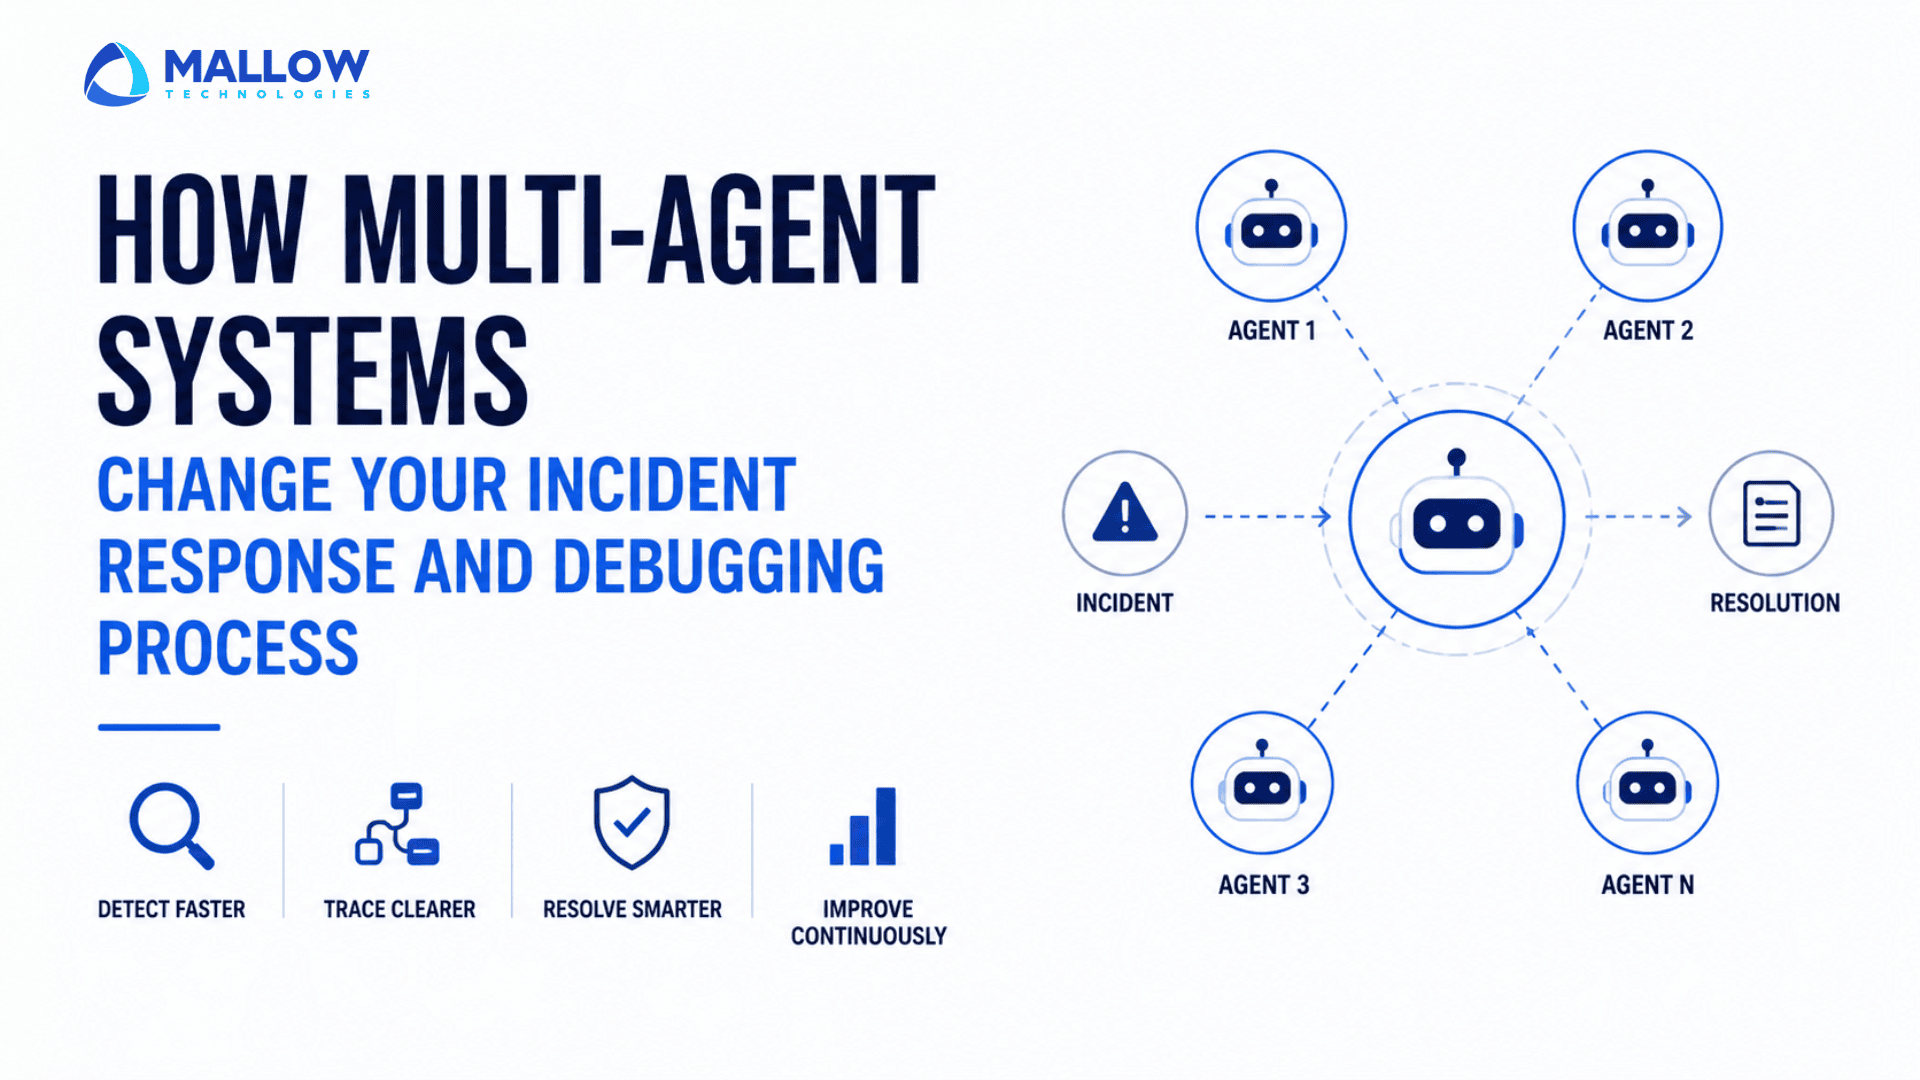
The first production incident in a multi-agent system almost always goes the same way. Something in the output is wrong. Someone files a bug. An engineer opens the logs. The logs show that every individual agent reported success. The orchestrator reported success. The output is still wrong. The engineer spends four hours in traces before […]
Imagine you are using an application and you ended up knowing that it wasn’t a secured one. For example, though the application appears to be legitimate but contains a hidden malicious payload that can perform various actions without the user’s knowledge. Would you go back using that application again? Of course you wouldn’t. Not at […]
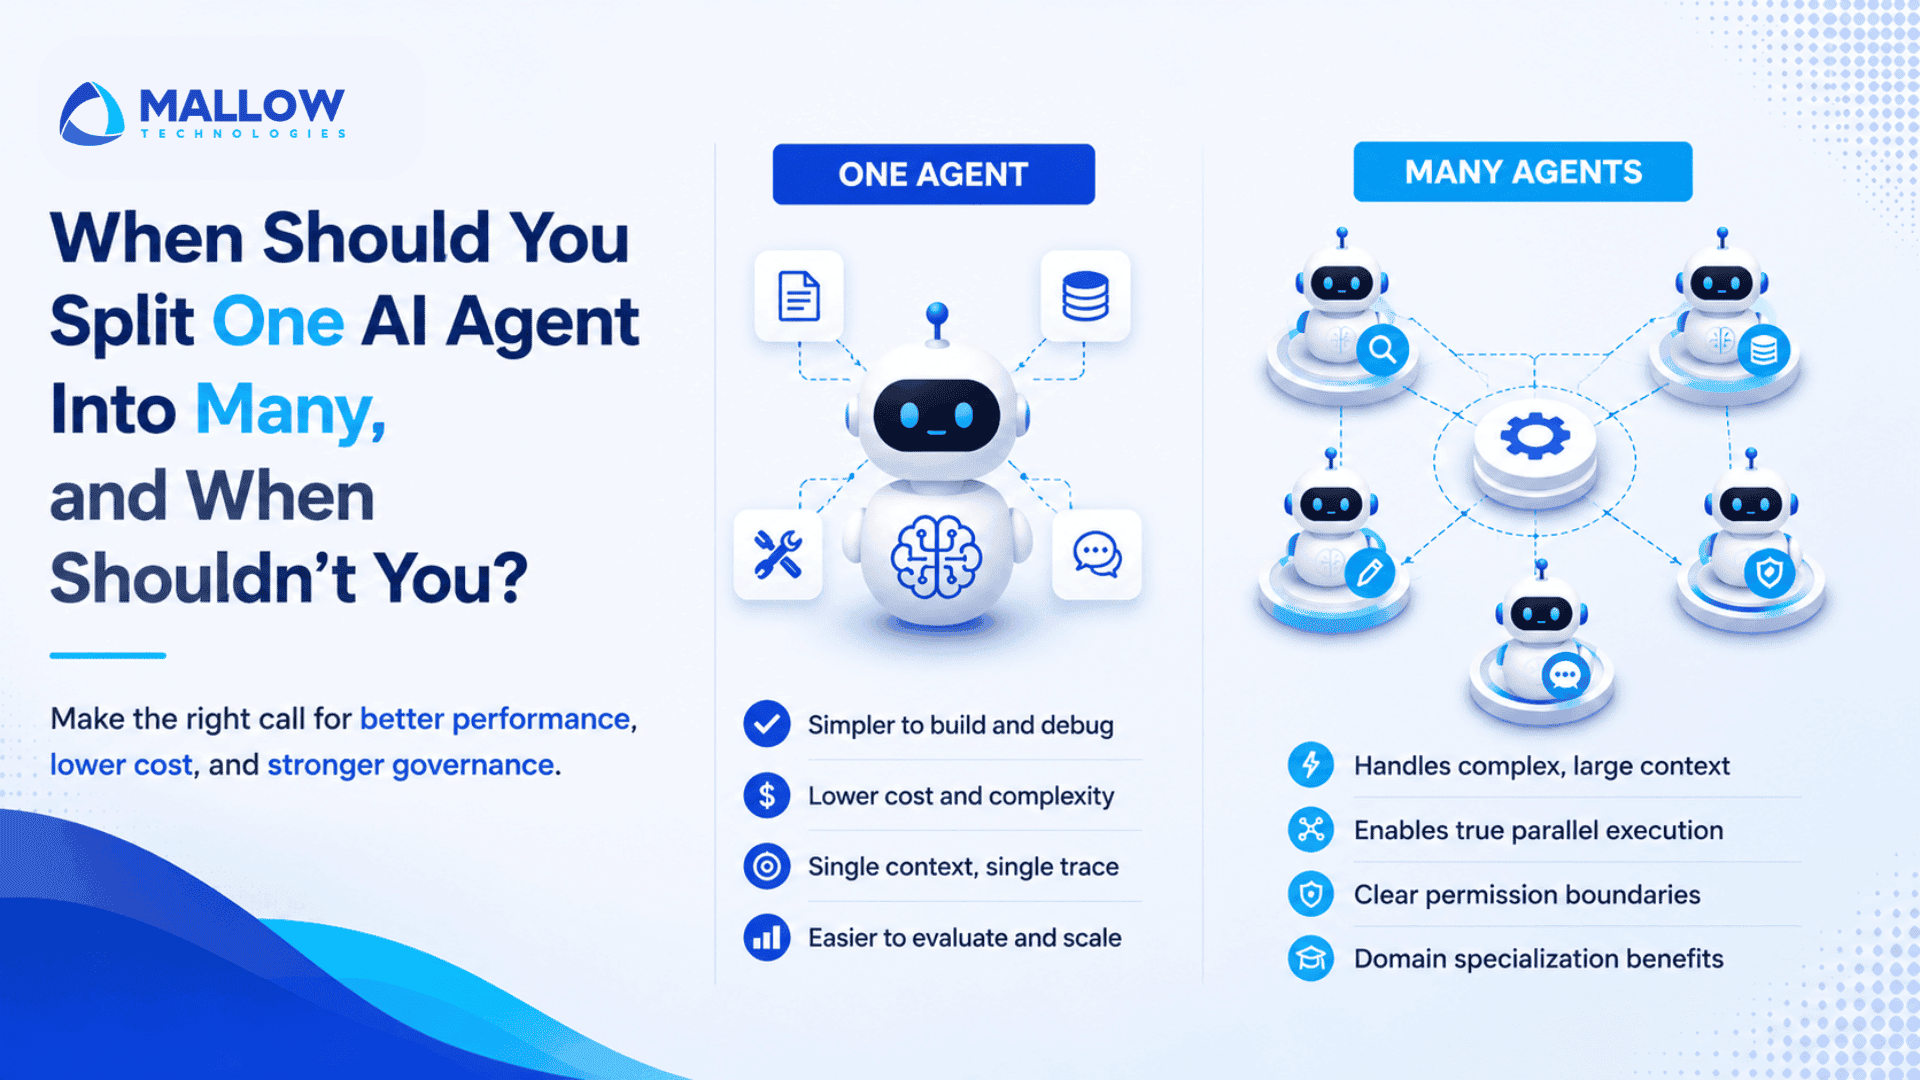
Once a single AI agent is working reliably, the next question many teams ask is whether it is time to split it into multiple specialised agents. At first glance, the idea seems logical. Multiple agents promise better specialisation, parallel execution, and greater flexibility. But in practice, a multi-agent architecture is not automatically better. In many […]
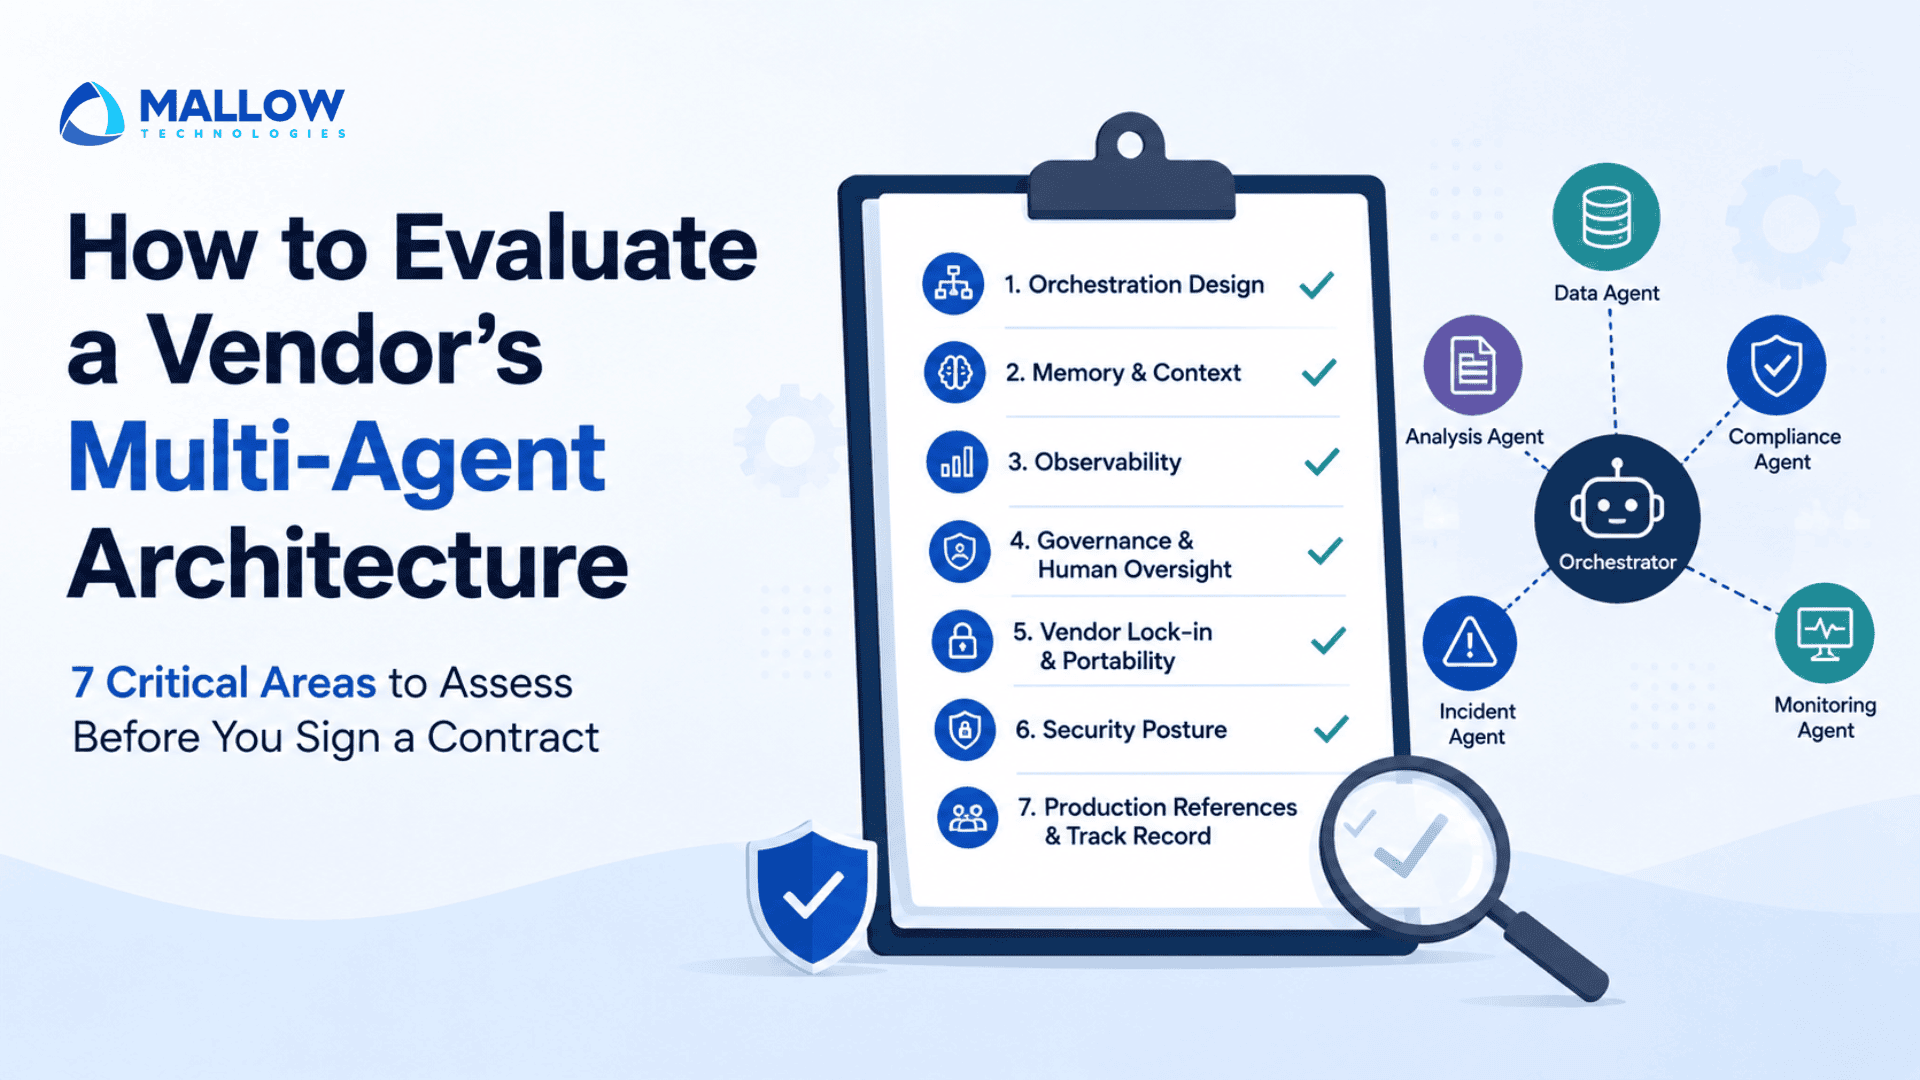
The demo worked perfectly. The vendor showed you agents handing tasks off to each other, a context layer that seemed to remember everything, and a governance dashboard that made the whole thing look controllable. You came away impressed. You are probably ready to sign. That is exactly the moment to slow down. Multi-agent AI systems […]
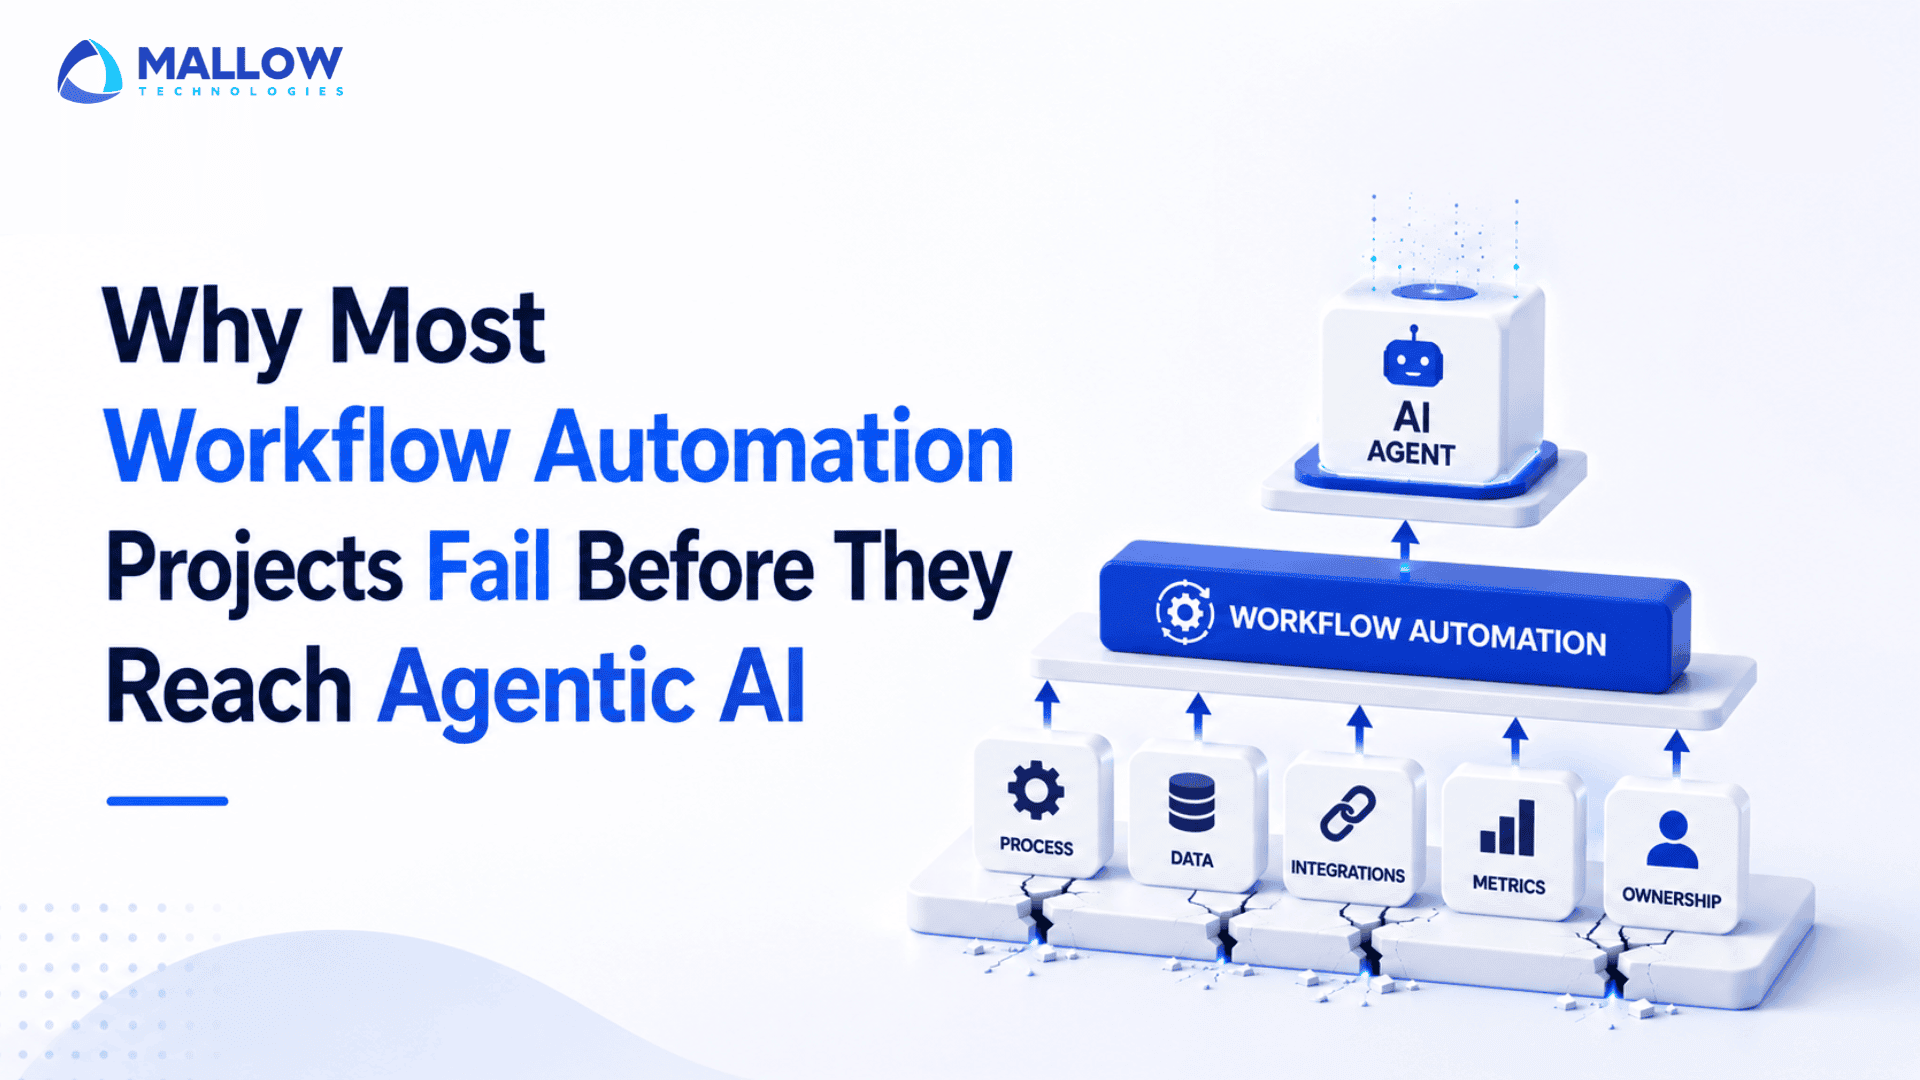
The diagnosis is almost always delivered too late. A team has spent six months building an automation workflow. It works in the demo. It breaks in production. An engineer spends two months patching it. It breaks again in a different place. Eventually the project quietly gets deprioritised in favour of something with cleaner momentum, and […]